Protecting Accounting & Finance Firms, Their Clients, and Their Reputation
Black Bottle IT learns how your firm works, from tax season crunch to year-round advisory, and builds a security program that protects client data and keeps you growing.
Accounting holds the second-highest cost of a Breach!
Your firm holds Social Security numbers, bank accounts, tax returns, and financial statements for every client you serve. That makes you a prime target. The average financial industry breach costs about $5.56 million, second only to health care. And with AI, attackers can now write a convincing phishing email in five minutes instead of 16 hours.

Phone
We’d love to hear from you, learn more about your firm, and share with you how a better security program can support the growth of your firm!
Main: 800-214-0957
Common Attack Methods!
Phishing & tax-season scams: fake IRS notices, client document requests, and e-signature links timed to your busiest weeks
Business email compromise: attackers hijack a client or vendor mailbox and send fake invoices or wire instructions; recent cases cost firms more than $200,000 each
Ransomware: encrypts tax software, client files, and backups right before a filing deadline, when firms are most likely to pay
Insider & third-party risk: seasonal staff, former employees, and software vendors who still have access to client data
Unvetted AI tools: staff pasting client financials into public chatbots, putting confidential data outside your control
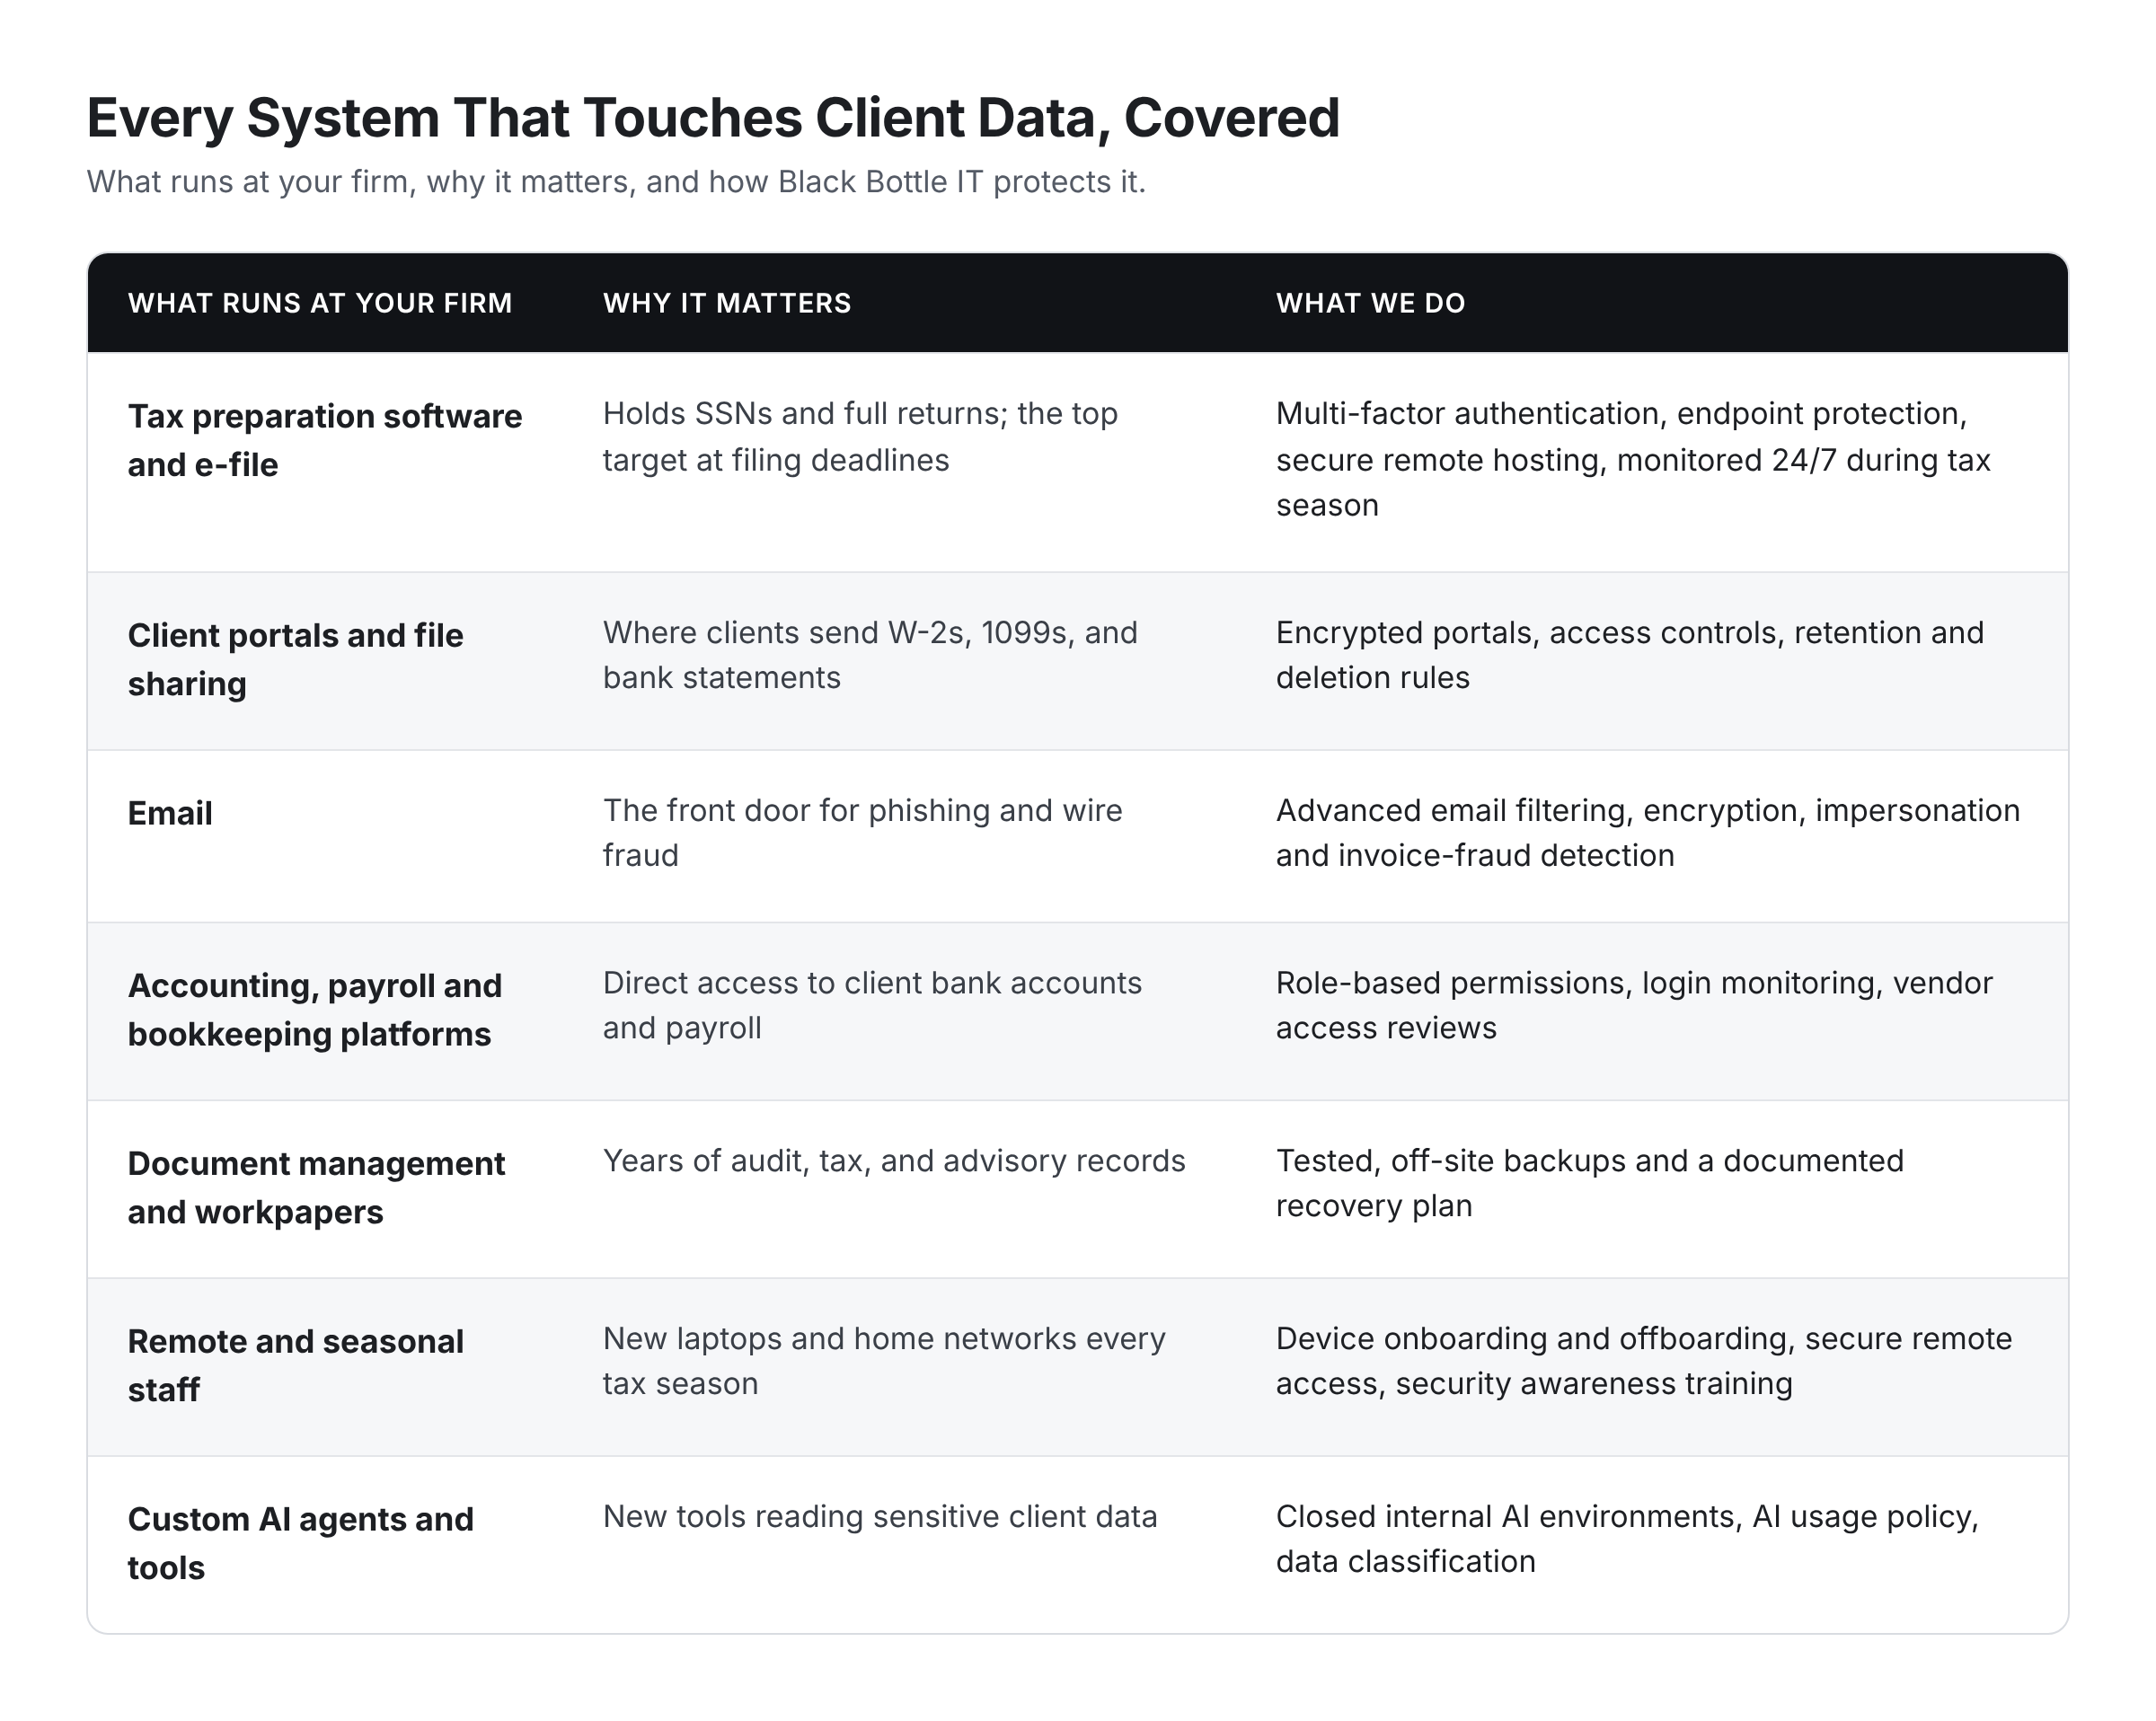
What Runs at Your Firm, and How We Protect It
Compliance & Auditing
Your Firm Is Legally Required to Have a WISP
Under the Gramm-Leach-Bliley Act, tax and accounting professionals are treated as financial institutions. The FTC Safeguards Rule requires them to keep a written, accessible information security plan, review and test it regularly, and name someone to coordinate it (IRS). Firms must also report certain security events affecting 500 or more people to the FTC, generally within 30 days of discovery.
We help you:
- Build and maintain your WISP using the IRS framework*
- Name and support your security coordinator
- Run regular risk assessments and document the results
- Meet cyber insurance and client due-diligence questionnaires with evidence ready
A SOC 2 Certified Partner
Your clients trust you with their most sensitive data, and you should expect the same from your IT partner. Black Bottle IT is SOC 2 certified, which means an independent auditor has reviewed our own security controls. When your clients, auditors, or insurers ask how your IT provider protects their data, you’ll have the answer.
Incident Response Plan
It’s Not a Matter of If, but When
We help organizations work through specific malicious events, avoid further damage, reduce recovery time, and mitigate cybersecurity risk, before an attack ever strikes. Your incident response plan becomes part of your WISP, so you’re covered on both compliance and recovery.
What’s included:
- Preparedness & Identification — Always up-to-date IT asset inventory, risk assessment, and a comprehensive risk management strategy.
- Detection & Alerts — Prompt detection of potential threats and cybersecurity events to mitigate damages before they escalate.
- Communication Plan — Coordinating with internal teams, external partners, and clients to notify and manage the impact of an incident, including required notices to the FTC, the IRS, and your state.
- Recovery Plan — A full plan of action to help your business recover and ensure the breach does not happen again.
AI Governance & Security
Building Custom AI Agents? Build Them Safely.
Firms are building AI agents to speed up tax prep, reconciliations, and client research. Those agents read the same confidential data your WISP is meant to protect. We protect your intellectual property and keep your people safe from the risks of unvetted public AI tools, building closed-loop, internal AI environments your team can use with confidence.
- AI policy development and enforcement
- Closed internal AI environments
- Data classification and sensitivity mapping
- Vendor AI risk assessments
- Employee AI usage training
- Compliance-aligned AI governance (HIPAA, CMMC, SOC 2)
The True Cost of a Breach
The average financial-industry breach costs about $5.56 million, well above the $4.4 million average across all industries**.
Beyond the direct financial impact, firms face serious consequences:
Client Trust & Reputation: Clients who hand over their tax returns and bank details expect them protected. One breach can cost a firm its client base and referrals.
Regulatory Consequences: FTC enforcement, state breach-notification penalties, and possible action by your state board of accountancy.
Business Disruption: Locked systems during tax season mean missed deadlines, extensions, and penalties for your clients, plus recovery costs for you.
Why Firms Choose Black Bottle IT
- SOC 2 certified — independently audited security, so you can answer your clients’ and insurers’ questions with confidence
- WISP and IR plans done for you — written, tested, and kept current
- Ready for tax season — extra monitoring and support when your workload peaks
- Secure AI — a partner who can help you adopt AI without risking client data
- 24/7 monitoring and an emergency breach hotline
Gap Assessment
Wondering where your business stands right now? Take our 3-minute Gap Assessment and get an immediate security score and roadmap. It’s fast, free, and eye-opening — a great first step toward closing the gaps before a bad actor does.
Ready to protect your clients and your firm?
Sources
- IRS: Security Summit reminds tax pros they need a WISP (IR-2026-92, Aug. 18, 2026) – GLBA, FTC Safeguards Rule, 500-person/30-day reporting, Publication 5708
- Journal of Accountancy: AI-powered hacking in accounting (Oct. 1, 2025) – $5.56M financial-industry breach cost, $4.4M average, 16 hours to 5 minutes phishing, $200K+ fake-invoice losses